SSL certificate problem: self signed certificate in certificate chain - the fix for git, curl, npm, pip and Node (reproduced with a private CA)
TL;DR
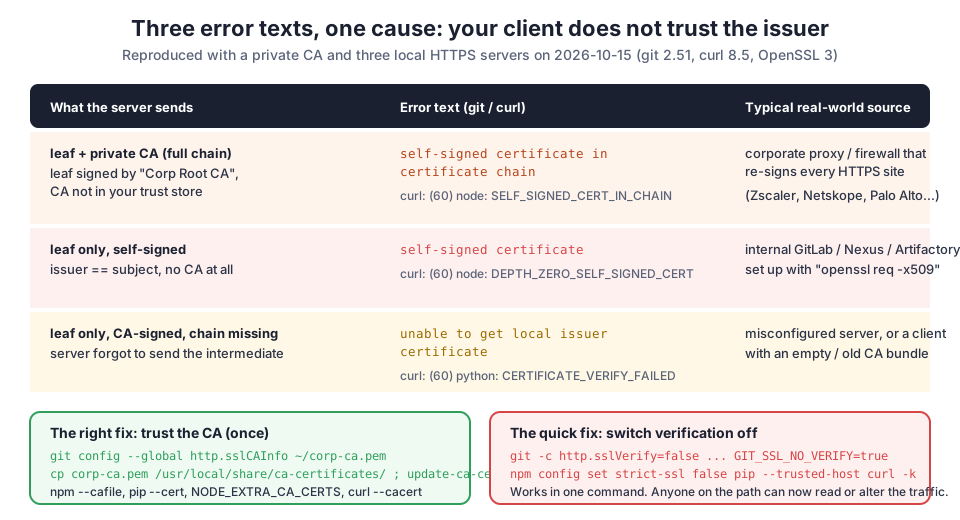
- The error means your client does not trust the issuer of the server's certificate. Three wordings, one cause:
self-signed certificate in certificate chain(a private CA signed it, and the server sent the chain),self-signed certificate(the leaf signed itself),unable to get local issuer certificate(the server did not send the intermediate). - Where it comes from: a corporate proxy or firewall that re-signs every HTTPS site with its own CA, or an internal Git, npm or PyPI server with a home-made certificate.
- The right fix is one file: get the CA certificate (from your IT team, or exported from the browser) and point the tool at it.
git config --global http.sslCAInfo ~/corp-ca.pem,curl --cacert,npm config set cafile,pip config set global.cert,NODE_EXTRA_CA_CERTS=.... Or add it to the OS trust store once and every tool follows. - The quick fix switches verification off:
git -c http.sslVerify=false,GIT_SSL_NO_VERIFY=true,npm config set strict-ssl false,pip --trusted-host,curl -k. It works in one command, and from then on anything on the network path can read or alter the traffic. - Modern git hides the detail. git 2.55 only prints
server certificate verification failed. CAfile: none; run the same URL throughcurlto see which of the three errors it is. - Every output below is from Ubuntu 24.04 with git 2.55, curl 8.5, OpenSSL 3.0.13, Node 22, npm 10 and Python 3.12, captured on 2026-10-15.
- Not your exact case? The closest post on this site is git@github.com.
I wrote the first version of this post in 2020 from inside a corporate network where every git clone failed with this error. The fixes I listed then still work, but I had never shown why the message appears or what the three different wordings mean. For this rewrite I built a private certificate authority, three local HTTPS servers that each misbehave in one way, and ran git, curl, npm, pip and Node against them. Every error and every fix below is real output from that run.
Table of Content
- Three errors, one cause
- How I reproduced it
- Git clone - what you see, and how to see more
- The right fix for git - trust the CA
- One fix for everything - the OS trust store
- Getting the CA certificate
- The quick fix - switching verification off
- npm - self signed cert in chain error code
- pip - certificate verify failed
- Node, Vagrant, PHP and Postman
- What broke when I ran this
- Conclusion
1. Three errors, one cause
| What the server sends | Error text | curl | Node | Typical source |
|---|---|---|---|---|
| leaf signed by a private CA, chain included | self-signed certificate in certificate chain | (60) | SELF_SIGNED_CERT_IN_CHAIN | corporate proxy or firewall (Zscaler, Netskope, Palo Alto, Fortinet) |
| leaf that signed itself | self-signed certificate | (60) | DEPTH_ZERO_SELF_SIGNED_CERT | internal GitLab, Nexus, Artifactory set up with openssl req -x509 |
| leaf signed by a CA, chain not sent | unable to get local issuer certificate | (60) | UNABLE_TO_GET_ISSUER_CERT_LOCALLY | misconfigured server, or a client with an empty CA bundle |
In every case the client did its job: it refused to talk to a server it could not identify. The fix is never "make the client stop checking"; it is "tell the client who the issuer is". The curl SSL certificate page, which curl prints a link to in the error, says the same.
2. How I reproduced it
A private CA valid for 365 days, a leaf certificate for localhost signed by it, and a purely self-signed one:
1$ openssl x509 -in leaf.pem -noout -subject -issuer
2subject=CN = localhost
3issuer=CN = Corp Root CA
4
5$ openssl x509 -in self.pem -noout -subject -issuer
6subject=CN = localhost
7issuer=CN = localhost
Then three HTTPS servers serving a bare git repository, a tiny npm registry and a pip index: port 8443 sends leaf plus CA, 8444 sends the self-signed leaf, 8445 sends the CA-signed leaf without the CA. The Corp Root CA is in none of the tools' trust stores, which is exactly the situation behind a corporate proxy.
3. Git clone - what you see, and how to see more
1$ git clone https://localhost:8443/repo.git c1
2Cloning into 'c1'...
3fatal: unable to access 'https://localhost:8443/repo.git/': server certificate verification failed. CAfile: none CRLfile: none
All three servers gave this identical line from git 2.55. The older, more specific wording that this post is named after now comes from curl, which git uses underneath:
1$ curl -sS https://localhost:8443/repo.git/HEAD
2curl: (60) SSL certificate problem: self-signed certificate in certificate chain
3
4$ curl -sS https://localhost:8444/repo.git/HEAD
5curl: (60) SSL certificate problem: self-signed certificate
6
7$ curl -sS https://localhost:8445/repo.git/HEAD
8curl: (60) SSL certificate problem: unable to get local issuer certificate
So when git says CAfile: none, run curl -sS https://<your git host>/ to learn which of the three cases you have. CAfile: none itself is a hint: git found no CA bundle at all, which on a minimal container image is a problem on its own (install ca-certificates).
4. The right fix for git - trust the CA
Point git at the CA file, once per command or permanently:
1$ git -c http.sslCAInfo=/tmp/ssl/pki/ca.pem clone -q https://localhost:8443/repo.git c-ok
2cloned
3
4$ git config --global http.sslCAInfo /tmp/ssl/pki/ca.pem
5$ git clone -q https://localhost:8443/repo.git c-ok2
6cloned
http.sslCAInfo is documented in git-config. If you only want it for one host, git supports http.<url>.sslCAInfo, for example git config --global http.https://git.corp.example.com/.sslCAInfo ~/corp-ca.pem, so public GitHub keeps using the system bundle.
For the purely self-signed server (port 8444) there is no CA to trust, so you trust the leaf itself:
1$ curl -sS --cacert /tmp/ssl/pki/ca.pem https://localhost:8444/repo.git/HEAD
2curl: (60) SSL certificate problem: self-signed certificate
3
4$ curl -sS --cacert /tmp/ssl/pki/self.pem https://localhost:8444/repo.git/HEAD
5ref: refs/heads/master
That is the same mechanism, with the server's own certificate as the "CA" file. If the next error is about SSH keys rather than TLS, that is a different problem: permission denied (publickey).
5. One fix for everything - the OS trust store
Adding the CA to the operating system's trust store fixes git, curl, pip and most other tools in one go. On Ubuntu and Debian:
1$ sudo cp /tmp/ssl/pki/ca.pem /usr/local/share/ca-certificates/corp-root.crt && sudo update-ca-certificates
21 added, 0 removed; done.
3
4$ curl -sS https://localhost:8443/repo.git/HEAD
5ref: refs/heads/master
6
7$ git clone -q https://localhost:8443/repo.git c-ok3
8cloned
No flags, no config. The file must end in .crt for update-ca-certificates to pick it up. On RHEL, Rocky and Fedora the equivalent is cp ca.pem /etc/pki/ca-trust/source/anchors/ && update-ca-trust; on macOS it is Keychain Access or security add-trusted-cert; on Windows, certutil -addstore Root ca.cer. Node and Java do not read the OS store on every platform, so they get their own flag below.
6. Getting the CA certificate
Behind a corporate proxy, ask IT for the root CA; they hand it out routinely. If you cannot wait, openssl shows the chain the server (or the proxy) sends:
1openssl s_client -connect git.corp.example.com:443 -showcerts </dev/null 2>/dev/null \
2  | awk '/BEGIN CERTIFICATE/,/END CERTIFICATE/' > chain.pem
The last certificate in that file is the one closest to the root; that is the one to trust. Without openssl, a browser can export it: open the site, click the padlock, view the certificate, and export the top entry of the chain in PEM or Base64 format. The screenshots from the original post still show the Firefox path:


7. The quick fix - switching verification off
I am showing these because they are everywhere on the internet and they do work:
1$ GIT_SSL_NO_VERIFY=true git clone -q https://localhost:8444/repo.git c-nov
2cloned
3
4$ git -c http.sslVerify=false ls-remote https://localhost:8445/repo.git
524a34f2fc28805c3132f3b3aaaa3f6a8e8934c15	refs/heads/main
6
7$ curl -sk https://localhost:8444/repo.git/HEAD
8ref: refs/heads/master
git config --global http.sslVerify false makes it permanent for every host, including GitHub. From that moment any proxy, hotel Wi-Fi or compromised router can present any certificate and git will accept it, which means it can serve you modified code. Use the one-command form in an emergency, fix it properly the same day, and never set the global option on a machine with push access.
8. npm - self signed cert in chain error code
npm uses Node's TLS, so it reports Node's error code:
1$ npm view left-pad version --registry https://localhost:8443/
2npm error code SELF_SIGNED_CERT_IN_CHAIN
3npm error errno SELF_SIGNED_CERT_IN_CHAIN
4npm error request to https://localhost:8443/left-pad failed, reason: self-signed certificate in certificate chain
Three fixes, in order of preference:
1$ npm view left-pad version --registry https://localhost:8443/ --cafile /tmp/ssl/pki/ca.pem
21.0.0
3
4$ NODE_EXTRA_CA_CERTS=/tmp/ssl/pki/ca.pem npm view left-pad version --registry https://localhost:8443/
51.0.0
6
7$ npm view left-pad version --registry https://localhost:8443/ --strict-ssl false
81.0.0
npm config set cafile ~/corp-ca.pem makes the first one permanent; the npm cafile option is the documented way. NODE_EXTRA_CA_CERTS has the advantage of fixing every Node program on the machine, not only npm (see section 10). strict-ssl false is the "switch it off" option.
9. pip - certificate verify failed
Python's wording is longer but contains the same three words:
1$ python3 -m pip download --no-deps -d /tmp/pipdl --index-url https://localhost:8443/simple/ requests==0.0.0
2WARNING: Retrying (Retry(total=4, ...)) after connection broken by 'SSLError(SSLCertVerificationError(1, '[SSL: CERTIFICATE_VERIFY_FAILED] certificate verify failed: self-signed certificate in certificate chain (_ssl.c:1000)'))': /simple/requests/
3...
4ERROR: No matching distribution found for requests==0.0.0
pip retries 5 times with increasing back-off before giving up, which is why this error takes a while to appear: on my Windows laptop, against the same kind of self-signed server, pip download took 40.7 seconds to fail with the default retries and 11.5 seconds with --retries 0, while curl and git clone failed in 2.4 seconds and 2.6 seconds. The fix is --cert, or permanently pip config set global.cert ~/corp-ca.pem:
1$ python3 -m pip download --no-deps -d /tmp/pipdl --index-url https://localhost:8443/simple/ --cert /tmp/ssl/pki/ca.pem requests==0.0.0
2Looking in indexes: https://localhost:8443/simple/
3Collecting requests==0.0.0
4  ERROR: HTTP error 404 while getting https://localhost:8443/simple/requests/requests-0.0.0.tar.gz
The 404 is expected: my fake index has no package file, so pip got through TLS and then found nothing to download. That is the proof that the certificate problem was solved. The quick fix for pip is --trusted-host localhost, which produced the same 404. pip's own HTTPS certificates page covers both. The pip side of this error, including the system-store option and Docker builds, has its own post: pip install trusted-host and CERTIFICATE_VERIFY_FAILED.
10. Node, Vagrant, PHP and Postman
Node itself reports the same code as npm, and NODE_EXTRA_CA_CERTS fixes any script:
1$ node -e "require('https').get('https://localhost:8443/',r=>console.log('status',r.statusCode)).on('error',e=>console.log(e.code, e.message))"
2SELF_SIGNED_CERT_IN_CHAIN self-signed certificate in certificate chain
3
4$ NODE_EXTRA_CA_CERTS=/tmp/ssl/pki/ca.pem node -e "..."
5status 200
The variable is documented on the Node CLI page and is read once at start-up, so set it in your shell profile or the CI job environment.
The following three were in the original post. I have not re-run them in 2026, so treat them as pointers rather than tested output:
- Vagrant:
vagrant box addgoes through Ruby's HTTP client;vagrant box add --insecure <box>skips verification, andSSL_CERT_FILE=~/corp-ca.pem vagrant upis the proper fix. - PHP (cURL extension): set
curl.cainfo = /path/to/corp-ca.pemandopenssl.cafileinphp.ini;CURLOPT_SSL_VERIFYPEER => falseis the quick fix. - Postman: Settings, General, "SSL certificate verification" can be switched off, or add the CA under Settings, Certificates, CA Certificates:

11. What broke when I ran this
I ran all of this as one script on a GitHub Actions runner on 2026-10-15. Three findings changed the post.
1. git no longer says "self signed certificate in certificate chain". The phrase this post is named after did not appear in any git output on git 2.55; every failure was the generic server certificate verification failed. CAfile: none CRLfile: none. The detailed wording lives in curl now. If you are searching for the exact git message you saw, it was probably from an older git, and curl is the quickest way to get the detail back.
2. The OS trust store fix needs the .crt extension. My first attempt copied ca.pem as is; update-ca-certificates reported 0 added. Renaming it to corp-root.crt gave 1 added, 0 removed and everything passed.
3. pip's retries make the failure slow. Five retries with back-off meant the pip error took 40.7 seconds to appear on my laptop against 2.4 seconds for curl, and in a CI log the five WARNING: Retrying lines are what you see first. Scroll to the end for the actual CERTIFICATE_VERIFY_FAILED line.
12. Conclusion
SSL certificate problem: self signed certificate in certificate chain is your client refusing a certificate signed by a CA it does not know. To summarise:
- Find out which of the three cases you have with
curl -sS https://host/; git itself only saysverification failed. - Get the CA (from IT,
openssl s_client -showcerts, or the browser) and trust it:http.sslCAInfofor git,--cacertfor curl,cafilefor npm,--certfor pip,NODE_EXTRA_CA_CERTSfor Node, or the OS trust store for all of them. - Keep the verification-off switches for emergencies, and never make them global.
If git fails for a different reason after the certificate is sorted, unable to update url base from redirection is the next most common one behind a corporate proxy, and adding an SSH key permanently avoids HTTPS for git entirely.
Did this save you a debugging session? Stay in the loop -
- Subscribe on YouTube - every post here has a screen-recorded companion video.
- Code on GitHub - the repositories, Terraform and scripts behind these posts.